
Be smarter than the average angler
In short: phishing is a message, call or website that pretends to be someone you trust (your bank, a courier, your boss, a well known brand) so that you hand over a password, a code or card details, or install something. The warning signs are almost always the same: urgency, a request for data or money, and a link or QR code you did not ask for. Do not click; open the official app or website yourself, and never share a verification code with anyone.
This guide is part of the series Attack vectors: the doors scammers use to get to you.
Table of Contents
Introduction
The term “phishing” is derived from “fishing” and was coined in the mid-1990s. The analogy is based on the concept of fishing for potential victims by luring them with bait. Here is a short look at the origin and development of the term:
- Early use in hacker culture. The term began to be used in the hacker community to describe “fishing” for sensitive information such as passwords, financial details or other personal information by masquerading as a trustworthy entity.
- AOL and early attacks. One of the earliest documented uses of the term was related to attacks on America Online (AOL). Scammers sent messages to AOL users, posing as AOL staff, and asked for their login credentials. They called it “phishing” because they were casting a broad net and hoping to catch a few unsuspecting users.
- Evolution of the term. The spelling “ph” instead of “f” is rooted in the hacker subculture, where such alterations were common, similar to “phreaking”, which describes hacking phone systems.
- General adoption. By the late 1990s and early 2000s, “phishing” had entered the broader cybersecurity vocabulary, as phishing scams increased and began to target a wider range of online services and users.
The fishing analogy, combined with the hacker culture’s taste for playful misspellings, produced a word that captures the deceptive and predatory nature of these attacks.
Phishing types
Phishing has evolved over the years, becoming more sophisticated and harder to detect. Here are the most common types of phishing:
Email phishing
Email phishing is the most widespread type of phishing attack. Cybercriminals send mass emails that appear to come from trusted sources like banks, social media sites or online services. These emails often create a sense of urgency, asking recipients to click on a link to confirm credentials or download an attachment. Once the victim takes the bait, they are redirected to a fake website where their personal information is harvested, or they download malware onto their device.
Spear phishing
Unlike generic email phishing, spear phishing targets specific individuals or organizations. Attackers gather information about their victims through social media, company websites and other sources to craft personalized emails or phone calls that appear legitimate. By using details the victim would recognize, such as their name, job title or recent activities, spear phishing has a higher success rate. The goal is often to gain access to sensitive company data or personal information.
Smishing (SMS phishing)
Smishing uses fraudulent text messages. They typically appear to come from banks, delivery companies, postal services or well known brands, and contain a link with instructions to follow. When the victim responds, they are tricked into providing personal information, paying a small “fee” or installing malicious software. Because people tend to trust text messages more than emails, smishing can be particularly effective. Read the full guide: smishing, how fake text messages work and how to protect yourself.
Vishing (voice phishing)
In vishing, attackers call pretending to be from banks, tech support or government agencies. They use social engineering to convince the victim to reveal account numbers, passwords or personal identification numbers, or to transfer money or install software, often by playing on fear (for example, that a loved one is in trouble). Read the full guide: vishing, how fake phone calls work and how to protect yourself.
QR code phishing (quishing)
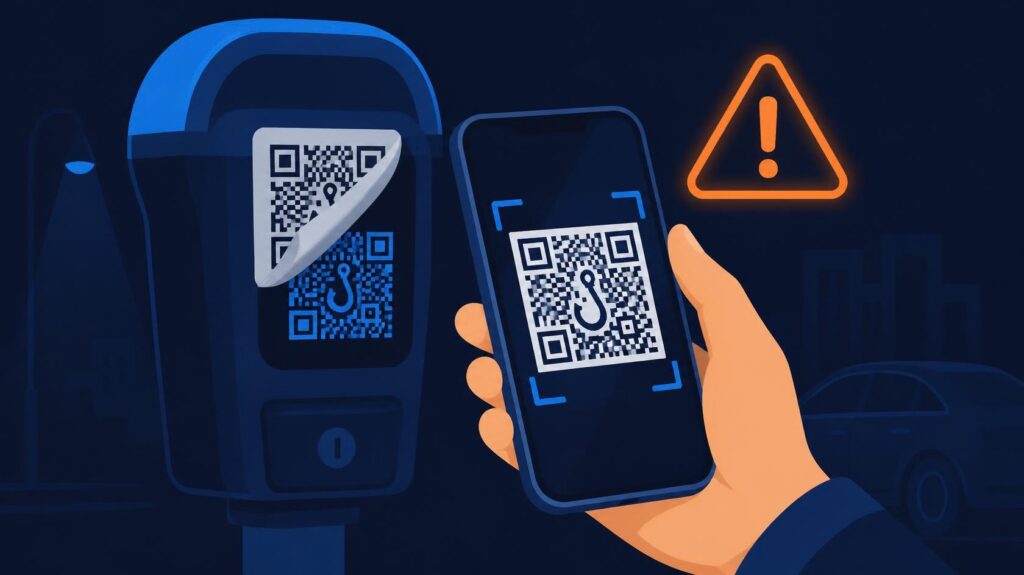
Quishing hides the phishing link inside a QR code: in an email, a text message, a fake parking ticket or a sticker placed over a real code on a parking meter or restaurant table. You cannot read a QR code before you scan it, and email filters that check links often do not check images, so this kind of bait gets through more easily.
Clone phishing
Imagine a fisherman casting his net into the water. He knows that fish are more likely to swim into a net that looks familiar and safe. Similarly, cybercriminals create cloned websites and emails that copy legitimate ones, often those of famous brands. Since the website or message looks familiar, people are more likely to trust it and act on it. Clone phishing is particularly insidious because it uses the trust the victim already has in the legitimate brand. Buying something on such a website can cost you your card details.
What's new in 2026
- Phishing keeps growing. The Anti-Phishing Working Group counted 971,181 phishing attacks in the first quarter of 2026, up 13.8% from the last quarter of 2025. Scams increased on every social media platform, and phishing by phone and text message (vishing and smishing) rose 15%.
- Two-factor codes can be stolen too. In March 2026, Europol and Microsoft took down Tycoon 2FA, a phishing service rented out to criminals since 2023. Its fake login pages sat between the victim and the real site and captured passwords, one-time codes and session cookies in real time. It was linked to attacks on nearly 100,000 organizations, and at its peak it accounted for about 62% of the phishing attempts Microsoft blocked. Two-factor authentication is still essential, but a code typed into a fake page protects nothing.
- Fake parking fines with QR codes. In 2026, scammers in several US states sent fake traffic violation texts and left fake parking notices with QR codes on cars. The code leads to a payment page that steals card details. A QR code is just a link you cannot read, so treat it like one.
The bait changes, the trap does not: whatever arrives, open the official app or website yourself instead of following the link.
Phishing exploits emotions
Phishing attacks often rely on urgency and fear to make victims act quickly, without thinking. Here is how these tactics work.
Creating a sense of urgency
- Immediate action required. Messages say things like “Your account will be locked in 24 hours” or “You must verify your information immediately”. The pressure makes victims respond before their usual caution kicks in.
- Limited time offers. Fake offers that seem too good to miss, such as “Claim your reward within the next hour!”, play on the fear of missing out.
Instilling fear
- Threats of negative consequences. For instance: “Your bank account has been compromised. Verify your details now, or risk losing your funds.” The fear of losing money or of identity theft drives victims to act.
- Urgent security alerts. Fake alerts claiming that your account has been hacked cause panic. Victims follow the instructions to “secure” their account and hand their data to the attackers.
Social engineering
Social engineering manipulates human behavior and trust. Phishing attackers use it to get victims to reveal confidential information:
- Authority figures. Phishers pose as banks, government agencies or company executives. The borrowed authority makes victims more likely to comply.
- Familiar contacts. Attackers spoof the email address or phone number of someone you know, so the request seems to come from a friend or colleague.
- Building rapport. Attackers chat with the victim to build familiarity and trust, often using personal details found on social media.
- Pretexting. Phishers invent a scenario, for example a “tech support” call that needs your login details to fix a problem that does not exist.
The impact of phishing
Phishing is not a minor inconvenience; its consequences can be devastating for both individuals and organizations.
Impact on individuals
- Financial loss. With access to your banking information, attackers can empty accounts, make unauthorized purchases or commit other fraud.
- Identity theft. Stolen personal information can be used to open accounts or make transactions in your name, and fixing that takes a lot of time and effort.
- Emotional stress. The sense of violation and the financial consequences can cause long lasting anxiety.
- Loss of sensitive information. Identification numbers, health records and other sensitive data can be used for blackmail or further fraud.
Impact on organizations
- Financial costs. Direct theft of funds, the cost of investigating and fixing the breach, and possible fines under data protection rules.
- Damaged reputation. Customers and partners may lose trust in the company’s ability to protect their information.
- Operational disruption. Phishing can lead to ransomware or compromised systems, with downtime and expensive recovery.
- Legal and regulatory consequences. Failing to protect data adequately can lead to legal action and fines under laws such as GDPR or HIPAA.
- Impact on employees. Employees who were tricked may feel stress and guilt, which affects morale and, in severe cases, their jobs.
Case studies
Two well known cases show how attackers work and what it costs the victims.
The Target data breach
Overview: in late 2013, the US retailer Target suffered one of the largest data breaches in history, affecting about 40 million credit and debit card accounts and 70 million customer records.
How it happened:
- Initial phishing attack. The attackers first compromised Fazio Mechanical Services, a third party vendor that provided HVAC services to Target, through a phishing email that installed malware on the vendor’s systems.
- Network infiltration. Using the vendor’s stolen credentials, they entered Target’s network and installed malware on its point of sale (POS) systems to capture card data at checkout.
- Data exfiltration. Over several weeks, the attackers copied the stolen data to external servers.
Impact: Target reported about $292 million in gross breach related expenses, covering legal fees, settlements and security upgrades, along with lasting damage to customer trust.
The Ubiquiti Networks fraud
Overview: in 2015, the technology company Ubiquiti Networks lost $46.7 million to a business email compromise scam.
How it happened:
- Email spoofing. The attackers impersonated company executives and emailed the finance department, asking for urgent wire transfers to overseas accounts.
- Social engineering. The emails copied the language and details of real executive messages, so the finance staff complied without suspicion.
- Funds transfer. Over time, the finance department sent transfers totaling $46.7 million.
Impact: Ubiquiti recovered $8.1 million with the help of law enforcement. The incident led to an internal investigation and to changes in the company’s payment controls.
Identify the phishing attempts
Phishing bait is designed to trick you into revealing information or clicking on malicious links. These checks help you spot it.
Email phishing
- Check the sender’s address. Look for misspellings or extra characters and view the full address, not just the display name. Be cautious when a “company” writes from a free email provider.
- Look for odd language. Poor grammar, an inconsistent tone or a generic greeting are warning signs, although AI now writes convincing phishing emails without mistakes.
- Do not click links. Hover over a link to see where it really goes, and use your own bookmarks to reach the sites you use often.
- Verify with the source. Contact the company using its official contact details, check your account independently, and confirm requests from people you know through another channel.
Smishing (SMS phishing)
- Scrutinize the sender. Be cautious with unknown or unusual numbers, and verify through official channels anyone who claims to be a known company.
- Beware of urgency. Take a moment before reacting to an urgent request for information or payment.
- Do not tap links. Treat links in text messages like email links: type the website address yourself.
- Do not share personal information. Reputable companies do not ask for sensitive data by text message.
Vishing (voice phishing)
- Be skeptical of unexpected calls. Hang up and call back on the official number.
- Do not share sensitive information. Legitimate companies will not ask for passwords or codes over the phone.
- Remember that caller ID can be faked. A familiar number on the screen proves nothing; trust your instinct and verify independently.
Spear phishing
- Personal details are not proof. Spear phishing uses information about you to seem legitimate; confirm with the supposed sender through a different channel.
- Look for things that do not fit. Be wary of messages that do not match the usual context, language or tone of the sender.
- Do not answer unsolicited requests for data. Verify the request through official channels first.
Cloned websites
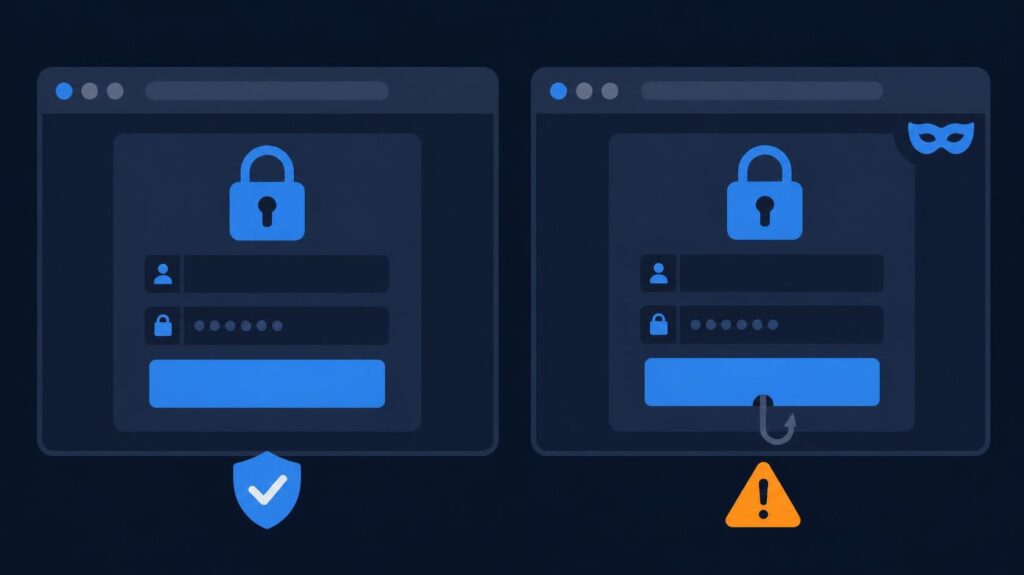
- Check the address carefully. Look for small misspellings or extra characters in the web address. A padlock and “https” only mean the connection is encrypted, not that the site is honest: most phishing sites have them too.
- Look at the details. Cloned websites may have low quality images, wrong logos or unusual layouts.
- Verify before entering anything. Do not enter personal or card details on a site you reached from a link; open the official site yourself.
Cybercriminals keep changing their tactics, so staying informed and cautious is your best protection.
Protect yourself from phishing
A few habits protect your accounts and money even when a phishing message gets through.
Use strong, unique passwords
- Make them long and hard to guess. Avoid birthdays, common words or sequences.
- Use a different password for each account. This limits the damage if one account is compromised.
- Use a password manager. It creates and stores strong passwords, so you do not have to remember them.
Enable two-factor authentication (2FA)
- Add a second step. Turn on 2FA wherever you can: on email, banking and social media accounts, including Facebook, Instagram, LinkedIn and eYou.social.
- Prefer authenticator apps to SMS. SMS codes can be intercepted through SIM swapping.
- Never type a code on a page you reached from a link. Phishing kits can now capture one-time codes in real time. Passkeys, where available, cannot be phished this way.
- Keep your recovery options up to date. An up to date phone number and email help you get your account back.
Keep your software updated
- Install updates promptly for your operating system, browser and apps, or turn on automatic updates.
- Use reputable security software that also blocks known phishing sites.
Be skeptical
- Question unexpected requests for personal or financial information, even when they seem to come from a trusted source.
- Verify independently by contacting the organization through its official channels.
- Think before you click on links or attachments in unexpected messages.
- Stay informed about current scams. Read also how to protect your social media accounts.
Steps to take if you fall victim
If you realize you have fallen for a phishing scam, act immediately to limit the damage.
Report the incident
- Tell your employer right away if you used a work account or device, so the IT or security team can contain the breach.
- Report it to the authorities: the police or your national cybercrime or cybersecurity authority (in Romania, DNSC at 1911).
- Notify the company that was impersonated. It may have specific steps to help you.
- Mark the message as phishing in your email app to help block future attacks.
Change compromised passwords
- Change the password of every affected account, on the real site, and everywhere you reused it.
- Turn on 2FA if it was not already on.
- Check for unauthorized access: review recent activity and settings, and sign out of all other sessions.
Watch your money
- If you entered card details, call your bank and block the card.
- Check your bank and card statements and report any transaction you do not recognize.
- Turn on transaction alerts with your bank, and consider a credit freeze if your identity data was exposed.
Warn your contacts
- Tell your contacts that your account was compromised and that they should ignore suspicious links sent in your name.
- Post a warning on your social media accounts if they were affected.
- Secure your other accounts and update their passwords if needed.
Frequently asked questions
What is phishing in simple terms?
A fake message, call or website that pretends to come from someone you trust, to get your passwords, codes, card details or money.
I clicked a phishing link. What should I do?
If you entered nothing, close the page and run a security scan. If you entered a password, change it right away on the real site and everywhere you reused it, and sign out of all sessions. If you entered card details, call your bank and block the card.
Does two-factor authentication stop phishing?
It stops most attacks, but not all: some phishing kits capture the code in real time. Never type a code on a page you reached from a link, and use passkeys where they are available.
How do I report a phishing message?
Use the “Report phishing” option in your email app, report scam texts to your mobile carrier, and tell your national cybersecurity authority (in Romania, DNSC at 1911).
Additional resources
Official guides
- Federal Trade Commission (FTC): Phishing guide
- FBI: Spoofing and phishing
- CISA: Phishing guidance
- UK National Cyber Security Centre (NCSC): Phishing guidance
Sources for 2026
- APWG: Phishing Activity Trends Report, Q1 2026
- Help Net Security: Authorities pull plug on Tycoon 2FA phishing-as-a-service platform (March 2026)
- gHacks: Traffic violation scam texts now use QR codes (April 2026)
- Hoodline: Fake parking tickets with QR codes (September 2026)
Recommended tools
- Password managers: 1Password, Bitwarden, Keeper.
- Authenticator apps: Google Authenticator, Microsoft Authenticator.
- Anti-phishing browser extensions: Netcraft, Avast Online Security, Bitdefender TrafficLight.
- Security software: Norton, McAfee, Bitdefender Total Security.
More on related scams: attack vectors, deepfakes and fake trading platforms.
Download the free PDF guide: How to navigate the waters of phishing attacks
About the author
Brîndușa Maria, Senior Software Test Analyst, ISTQB® Certified Tester Advanced Level Test Analyst (CTAL-TA). I write about how to recognize online scams. LinkedIn
Note: this article is based on my research and professional experience. I used artificial intelligence tools for drafting and editing.

📢 Share the knowledge, stay safe! 🔒✨ Use the share buttons below and help others stay safe online. The more we know about online scams, the better protected we are! 🚀💙
